Access for People and Systems
Secure, simple and centralized access to the most critical tools and environment, without compromising control.
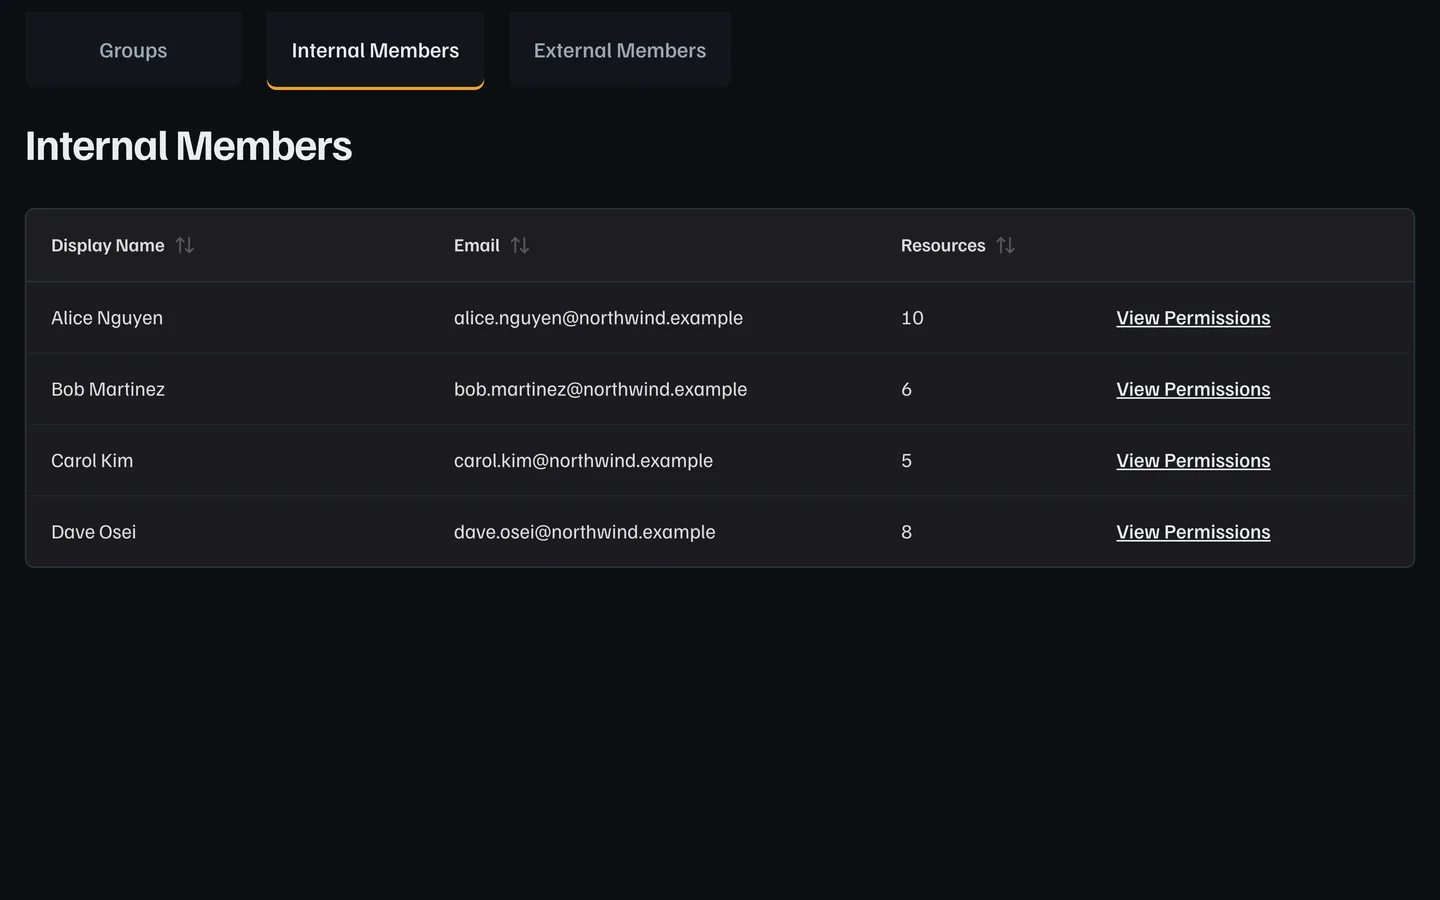
How Infrastream Manages High-Privilege Access
High Privilege Access Management (HPAM) is a modern security practice focused on managing elevated access rights across cloud-native environments. It ensures that both humans and systems are granted the right level of access to sensitive infrastructure, only when needed, and never more than necessary.
In a world where infrastructure is increasingly dynamic and distributed, HPAM becomes critical for reducing security risk, improving compliance, and simplifying operational workflows.
Why Automated Access Matters in the Age of AI
As AI-driven workflows scale, manual access management creates operational bottlenecks and security gaps. Infrastream automates this process by replacing manual provisioning with validated pull requests at the organization level.
Each access change arrives as a pull request, a written change you can read. Not yet: an approval before the change is applied is not enforced on every path.
How Infrastream Manages Access
Infrastream embeds identity, role-based access, and policy-driven authorization directly into the infrastructure layer. By making access control a native architectural requirement, Infrastream eliminates configuration gaps and reduces the management overhead of third-party security layers.
Native OIDC Authentication across platforms:
Infrastream directly manages secure identity authentication using OpenID Connect, eliminating the need for external identity bridges—reducing complexity and risk.
Role-based Access Control (RBAC) with fine-grained permissions:
Assign precise permissions to users and systems based on roles, ensuring the right level of access at all times.
Policy-based Authorization that mitigates common API vulnerabilities:
By managing your authentication engines and validators inside the service mesh, Infrastream proactively prevents the most frequent authorization issues found in the OWASP Top 10—out of the box.
Service Connectivity & Authorization:
Automate secure connections between services and workloads with strict, policy-driven authorization—no manual key sharing or insecure shortcuts.
Automated Provisioning & Deprovisioning of credentials:
Automatically create and revoke access credentials when users or systems join or leave, reducing manual errors and delays.
Audit Trails & Governance out of the box:
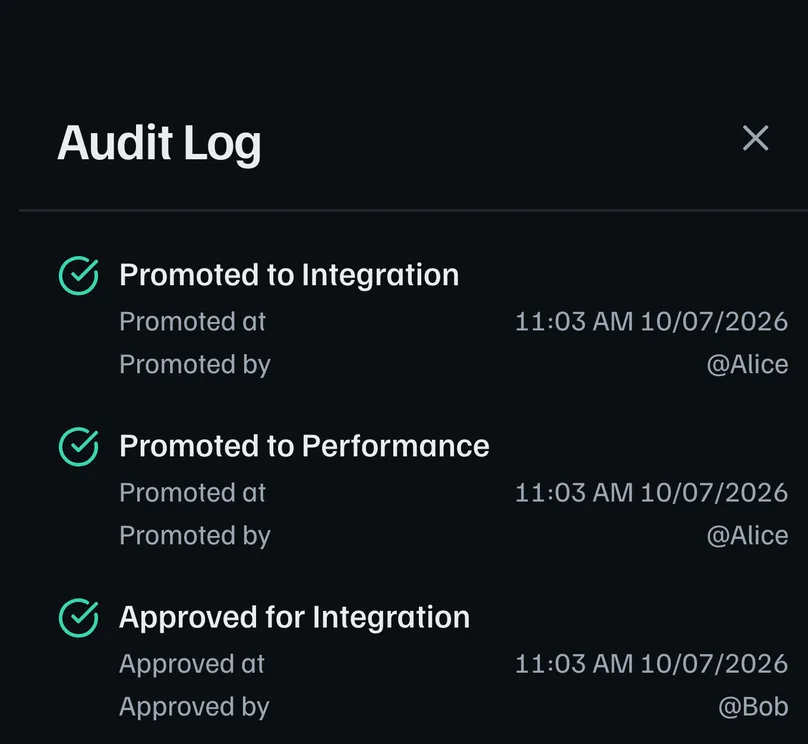
Track all access activity with built-in logging and compliance-friendly audit reports—no extra tooling required.
Native Access Control for the Tools Your Teams Use
When access control is built natively into tools like GitHub, GitLab, Google Workspace, GCP, and AlloyDB, security becomes seamless.
Centralized Control
One interface to manage access across tools. No more juggling permissions in every platform.
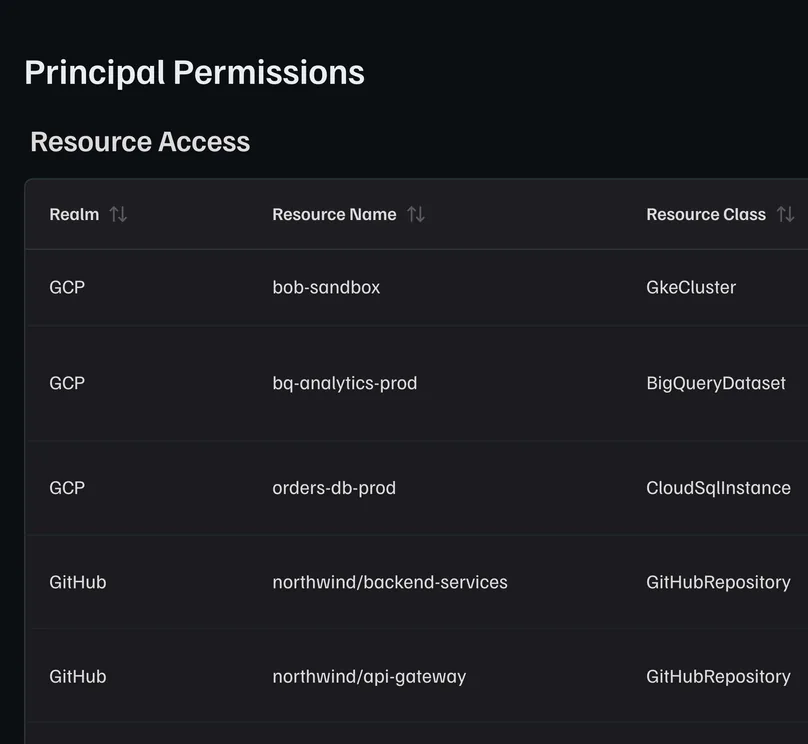
Built-In Visibility & Compliance
Access activity is tracked and logged automatically, helping you meet audit and regulatory needs without extra tools.
Secure by Default
We handle authentication via OIDC for employees, systems, and clients—secure and standardized.
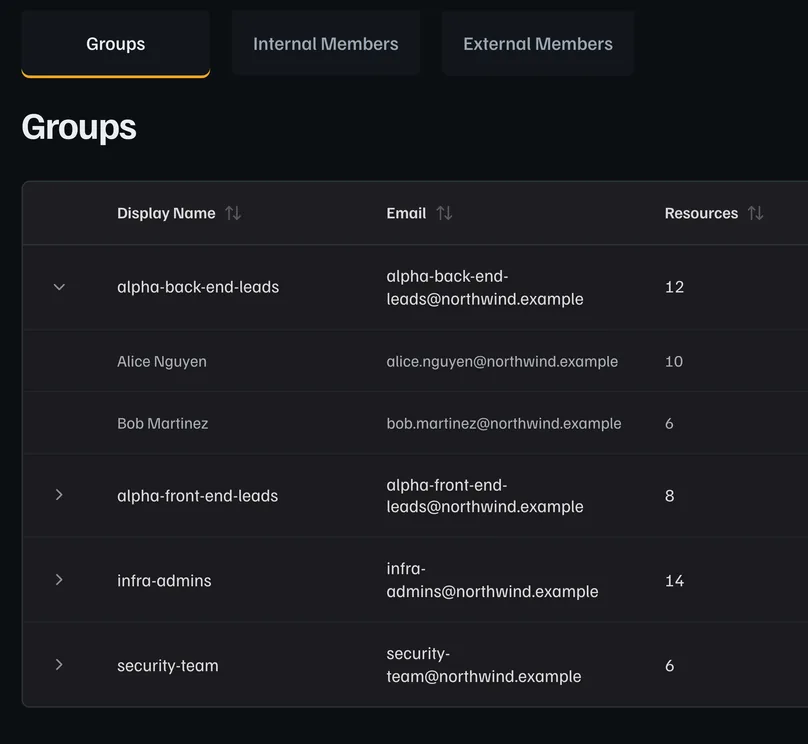
Faster Onboarding & Offboarding
Auto-sync roles and permissions.
No gaps. No manual work.


Why This Matters
Autonomous workloads and intelligent infrastructure require security to be a functional constraint rather than an add-on. Infrastream integrates High-Privilege Access Management (HPAM) directly into the infrastructure layer to enforce automation, auditability, and Zero Trust by default. This architecture ensures that all privileged actions are programmatically verified and logged, eliminating the risks associated with manual access control.